⚡️ 0-Day Alert: Node.js, PyPI, .NET, and others
The bug is now in active exploitation
CVE-2026-111497: Google Brotli buffer overflow
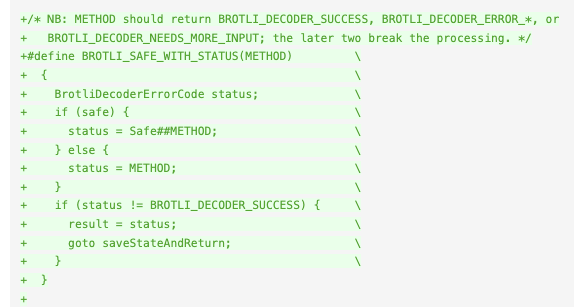
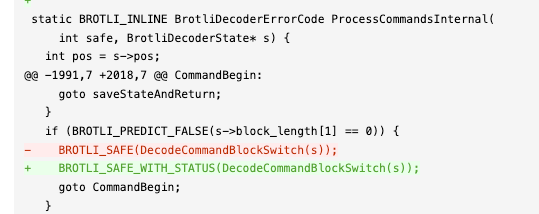
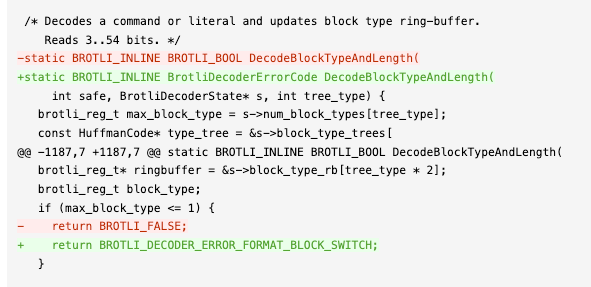
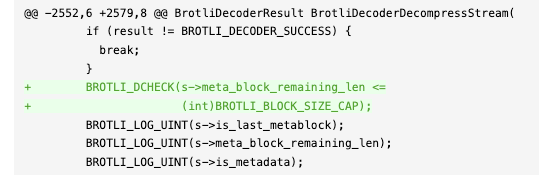
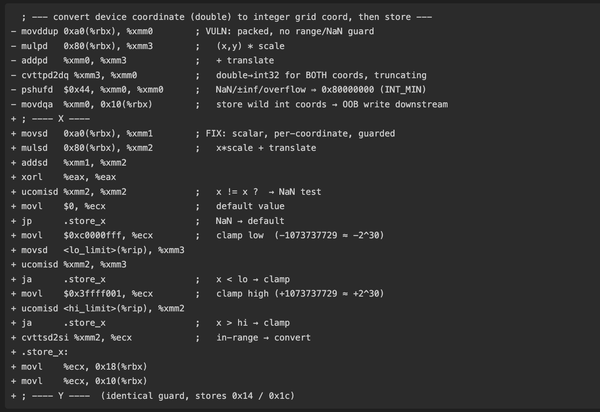
Logic error in input stream management of the 'br' decompression algorithm, leading to memory corruption and potential code execution. Impact is expressed through software that packages brotli library for input processing, such as Node.js and PyPI.
CWE-787 — Out-of-bounds Write (primary)
CWE-252 — Unchecked Return Value (secondary, contributing)
The bug is now confirmed in active exploitation. Stripe, Digital Ocean, and other digital infrastructure providers warned about it earlier.
More software products are likely affected than currently reported. Furthermore, the issue may persist indefinitely in older software which bundles brotli library but fails to merge the fixed version.
Current most dangerous attack vector - Node.js, where an exploit is remote and proven.
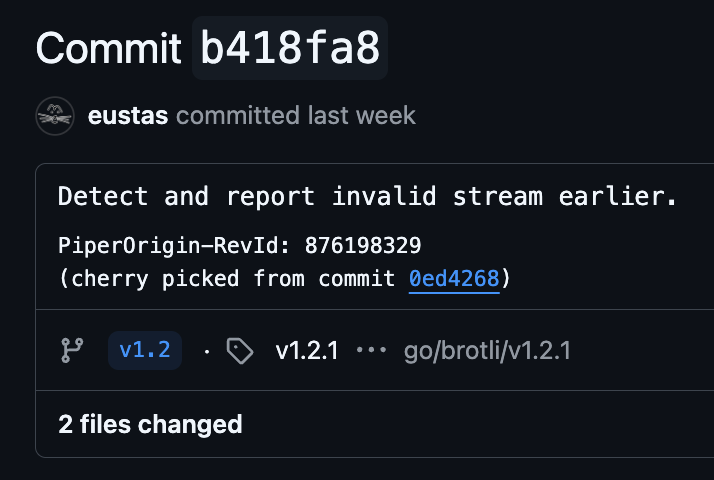
Brotli fixed versions: 1.0.10, 1.1.1, 1.2.1
Node.js: 22.23.4, 24.22.1, 26.12.1